Meat processing companies across the UK have fallen victim to cyber attacks following hackers targeting supermarket freezers throughout Europe. The National Cyber Security Centre (NCSC) has confirmed it is supporting the affected businesses and that the nationwide impact remains "minimal".
NCSC responds to incidents
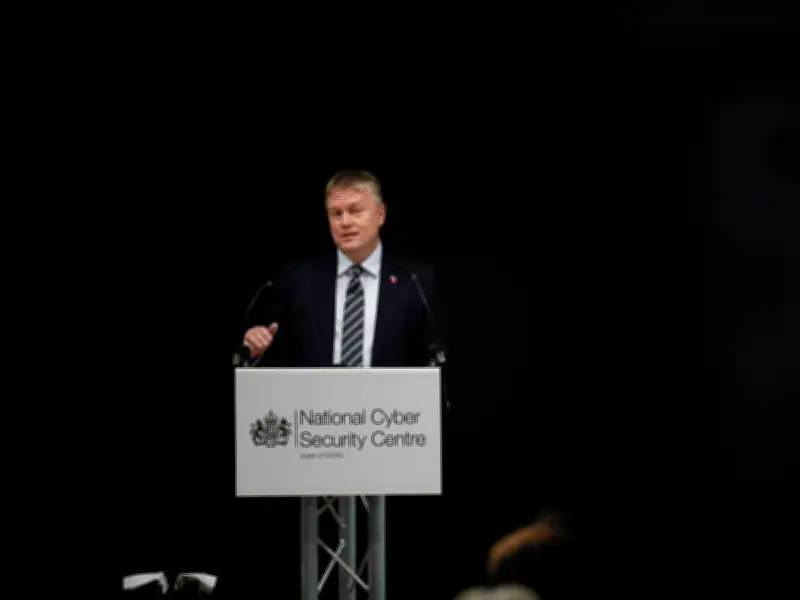
Speaking at the launch of the NCSC annual report on Tuesday, Paul Chichester, director of operations, said: "We're aware of those incidents in the UK, and obviously we're working with the affected organisations. We'll keep monitoring that. At the moment, the impact is minimal."
He continued: "We're working with organisations identifying existing vulnerabilities in the UK and trying to get those closed before somebody exploits them."
Impact on meat suppliers
The Association of Independent Meat Suppliers (Aims) revealed that a handful of its approximately 300 members had been affected by the breach, with refrigeration units warming up during the night. However, due to the typical operating patterns of abattoirs, the facilities were empty when this occurred, meaning no food products were compromised.
A spokesman for Aims explained that members using the same software as the affected European supermarkets had "unexpectedly become collateral" in the hack. "None who have been affected have lost any meat, but once again this must act as a reminder to all in the food industry, at whatever point in the supply chain they are, that their businesses may be seen by some as targets," he said. "We urge our members and the wider industry to vigilant."
Retailers urged to stay vigilant
No major supermarket chain is believed to have been directly affected by the hack. However, retailers are being urged to keep a close eye on their systems for potential vulnerabilities, ensure their software remains up to date, and have contingency plans in place should food produce need to be moved elsewhere.
Graham Wynn, assistant director of regulatory affairs at the BRC, said: "Retailers invest heavily in their cybersecurity and are currently working with the NCSC to ensure their fridges and freezers are secure as possible against potential attacks."
NCSC chief Dr Richard Horne revealed that his teams had been working through the night to warn British businesses that could be susceptible to such an attack. It has since emerged that the cyber attack targeting French supermarket refrigeration units exploited legacy technology connected to the internet using default passwords.
Speaking to an audience at the report launch in central London, he said: "Last night, we had people working through the night contacting organisations that we could see they had vulnerable technology exposed."
Dr Horne had earlier told BBC Radio 4's Today programme: "There are handfuls of organisations in the UK we've alerted and we're aware of a couple of impacts." When pressed on reports that some freezers in Britain had been switched to defrost mode, he said: "We don't know the full impact, but we can see there are a couple of instances where vulnerable technology has been exploited, and we will be working with those organisations to understand more."
Speaking about those responsible for the attack, he said: "It's too early for us to say at the moment and give a definitive answer." When asked whether it reinforces warnings from the Defence Secretary that people across the UK should be stockpiling supplies, he responded: "Absolutely. And we saw criminal attacks last year impact retailers in the UK. We know it can happen, and we've seen it across Europe. We see all sorts of impacts of cyber attacks, and because technology underpins everything, and because there is so much vulnerability in the technology we rely on because it's been underinvested in, we do need all organisations to look at what they rely on, to invest in renewal, and, at the end of the day, we work 24 by seven. We alert people. We intervene where we can. But, at the end of the day, it's your business. It's your charity. It's your life. You need to make the choice and choose wisely."
Warnings on AI-enhanced attacks
Delivering his speech to launch the report, Dr Horne cautioned that the UK has left itself exposed by pursuing a "tech on the cheap" approach for decades, as the NCSC warned that Britain faces the very real prospect of AI-enhanced attacks on critical national infrastructure within the next two years.
Ransomware hackers are "highly likely" to harness AI to target the UK by 2028, while hostile nations such as Russia and China will routinely deploy the technology in pursuit of their objectives by that point, the report concluded. Dr Horne said: "It is clear that our nation is living through a moment that, in hindsight, we will see as one of enormous consequence. A 'sliding doors' moment. A moment of choice. In the coming months, we face a real prospect of an unprecedented rise in the number of cyber incidents. But we must be clear that is not because AI has invented new ways to attack us, but because vulnerabilities that have been tolerated for far too long can now be discovered and exploited at a scale that was once unimaginable. And because far too many of our organisations and supply chains rest on weak technology and operational foundations."
He cautioned that business leaders who fail to act now will ultimately be forced to account for their inaction against a backdrop of empty supermarket shelves and widespread power cuts. "If leaders of organisations of every size and type do not take the responsibility now to make different choices, then they will one day have to look their investors, shareholders, employees, customers, suppliers, their families and friends in the eye and explain why, despite knowing the consequences, they failed to make the choices required. When food isn't on shelves, lights aren't on, businesses have gone under, we may have to explain that we saw the warning signs, understood the risks and still didn't make the right choices."
The NCSC annual report revealed that its incident management team handled 1,831 reports of cyber attacks this year, with 337 requiring support and 80 deemed nationally significant. The team also alerted 8,500 organisations after their systems had been breached by attackers, according to the report.
Dr Horne said: "For decades, we have collectively got away with doing tech on the cheap. End-of-life systems kept running for just one more year, well-needed upgrades pushed back as a 'cost efficiency', and technology providers failing to invest in security by design and default." He added: "Now that also carries through to the technology that underpins the automation of physical processes that are vital to modern life. Electricity switching, sluice gates in water facilities, dam operations, manufacturing lines, heating and refrigeration controls. Whilst they are not seen as traditional IT, they too are not built on the strong foundations they require. Their resilience and security is even more overlooked in investment decisions. Our resulting exposure as a society is huge and increasingly exploited in cyber attacks as we saw in the recent disruption of refrigeration units in supermarkets in France."
He warned that China is best-placed to deploy AI in targeting UK critical national infrastructure.