ASOS has warned customers that their personal information may have been accessed following a cyberattack involving a third-party platform. The online fashion retailer said it was investigating “unauthorised activity” after thousands of customers received alarming messages on Wednesday morning.
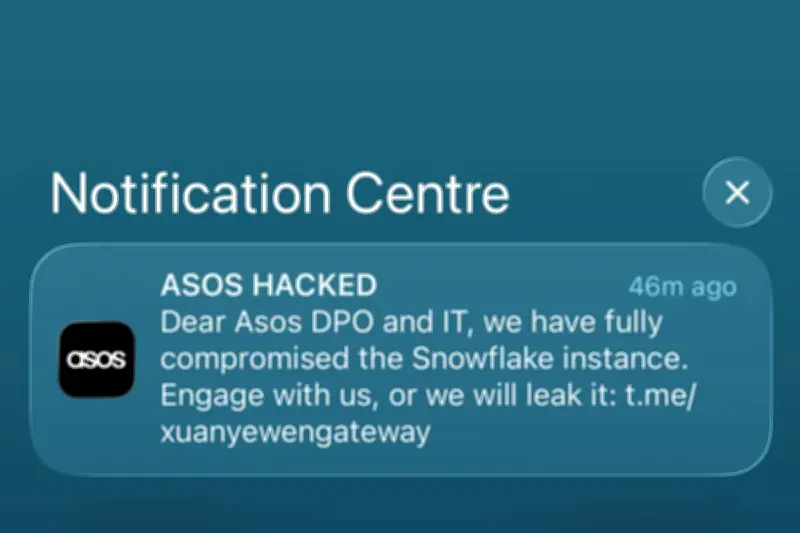
The notification, which appeared to be addressed to ASOS itself, read: “Dear Asos DPO and IT, we have fully compromised the Snowflake instance. Engage with us or we will leak it.” It also included a link to Telegram. A DPO, or data protection officer, is responsible for overseeing how an organisation handles and protects personal data.
Customer data 'may have been accessed'
In an update on Wednesday, ASOS confirmed that customer information, including names and contact details, “may have been accessed” as a result of the incident. However, the retailer said it does not believe payment card details or account passwords were affected. ASOS said it is continuing to investigate the incident.
On Tuesday afternoon, the company confirmed that an “unauthorised customer notification” had been sent out through its mobile app. In a statement, the company said: “We are investigating unauthorised activity involving third-party platforms that we use to communicate with customers.
“We took immediate action to restrict access to the notification platforms and are working with our internal and external specialist advisers, as well as all relevant authorities. Our website and app are operating as normal, with no current disruption to any aspects of our operations. Customer trust is incredibly important to us, and if the situation changes an update will be provided as appropriate.”
NCSC offers support
The National Cyber Security Centre (NCSC), a part of GCHQ, has offered ASOS assistance. The notification message sent out by cyber attackers refers to cloud firm Snowflake, which stores data for many major companies. Snowflake said it has “found no compromise” of its platform after launching an investigation following the notification message. “The investigation is ongoing and we will provide further updates as soon as more information becomes available,” a spokeswoman added.
ASOS told shareholders it has cyber security insurance with a large provider and said it is “too early” to quantify any potential impact on its trading. Shares in the company fell by more than 10% on Tuesday as a result. The UK is the group’s largest market, representing 49% of all revenues in the first half of the latest financial year. The fast fashion firm is currently undergoing a major turnaround programme in a bid to halt declining sales and return to profit.
Wider retail threat
It comes after a raft of UK retailers were targeted by cyber attackers over the past two years, including Marks & Spencer and Harrods.
Dr Richard Horne, chief executive of the NCSC, said: “The unauthorised notification sent out to Asos customers has brought into the light how cyber incidents do not simply affect big business but can have repercussions for individuals much more widely too. The NCSC has been in contact with Asos today to offer our support as the company investigates what has taken place.
“Individuals who received the notification should not click on any suspicious links and should stay vigilant to suspicious messages that may seek to take advantage of news of the breach. If you are worried about your personal data being impacted, we recommend following the advice set out at ncsc.gov.uk to help stay safe online.”